Thinking Ahead Blog

March 22, 2017
If you have received an SMS in the name of Banco BIC, Santander Totta or Montepio with a transfer notice or account activation notice, followed by a link to confirm it, you may have been the victim of phishing.
TweetIn recent days, a new wave of phishing attacks has emerged, that is, attempts to steal bank details through a simple SMS. Victims receive a message from an unknown number, in the name of Santander Totta, BIC or Montepio, requesting urgent action from the user.
Different messages have been used, in the name of several banks:
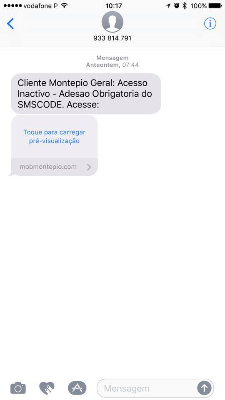
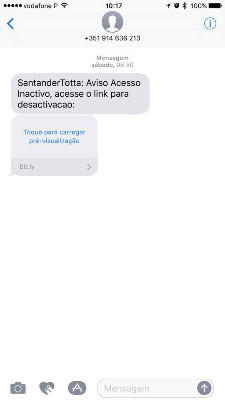
In this case, a message has been sent stating that the customer's access is "inactive" and that "mandatory enrolment in SMSCODE" is required, followed by a link to a fake page.
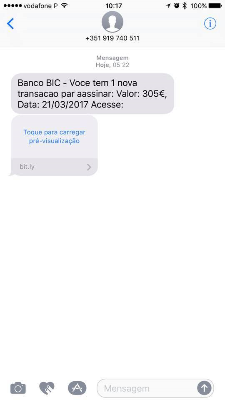
In this version, the user is faced with a message requesting a "transfer confirmation" for 305 euros or 310 euros, followed by the date and the fake link to "validate the transaction".
In the SMS in the name of Santander, an "Inactive Access" warning appears, followed by a link to a fake website.
If you have received an SMS similar to those described above, you should not click on the link suggested in the message. If you have already done so and entered your login details on the fake website, you may have been the victim of fraud.
In this situation, you are advised to contact your bank and the relevant authorities. You should also check your account balance and whether there have been any suspicious transactions. Even if no transaction has been made yet, one could happen at any time. Another step you should take is to change the login details for your online account, thereby preventing access by third parties.
This phishing attack uses the operators' messaging service to send the fraudulent link to the user. In practice, each bank's address is masked by a fraudulent service which, in the case of the Montepio SMS, is "montepio.jelastic.regruhosting.ru".
Phishing is one of the most frequent forms of online banking fraud and is usually carried out by e-mail. It occurs when a hacker poses as an institution or company and, through e-mail messages, phone calls or mobile text messages, tries to persuade a bank customer to disclose personal information, such as passwords and bank account numbers.
To avoid falling victim to phishing attacks, you should take some steps such as:

Written by:
Openlimits

Reporting your inventory to the Portuguese Tax Authority (AT) is a legal obligation and must be done by 30 January.
Know more >When inventory is not integrated, up to date and visible, companies lose much more than margin - they lose predictability, efficiency and responsiveness.
Know more >
We are very proud that Openlimits has received the SME EXCELLENCE (PME EXCELÊNCIA) award, alongside companies that are making the Coimbra Metropolitan Region an increasingly dynamic and competitive area.
Know more >
We are delighted to announce that Openlimits is now a Cegid Partner Gold in Portugal.
Know more >
Rua Princesa Cindazunda, nº. 55, Lote 16.6, Loja nº. 4
3030-503 Coimbra - PORTUGAL
tlf.: +351 239 940 150 (call to the Portuguese national landline network)
e.: geral@openlimits.pt
PORTUGAL | ANGOLA